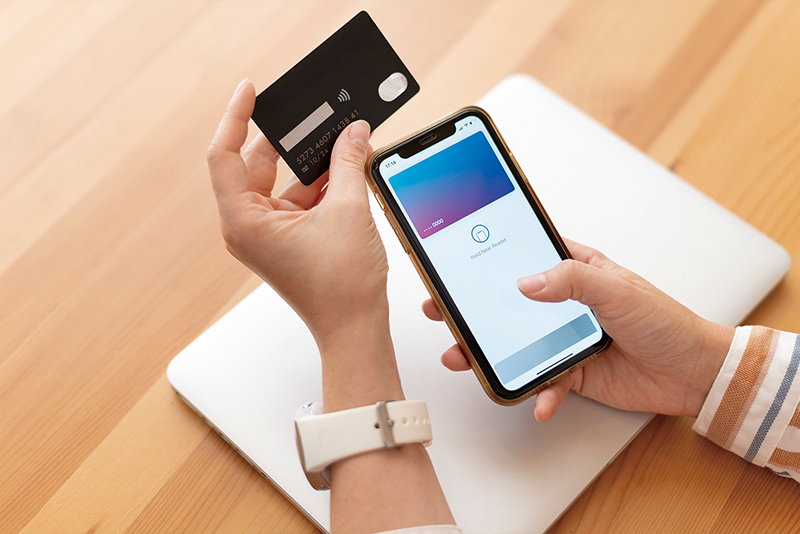
Tapping your card to your phone to make a purchase may seem harmless, but cybercriminals have found a way to turn contactless card taps into a dangerous scam. Researchers at Group-IB, a cybersecurity company, discovered a new type of malware called WindRelay that can capture contactless card information and send it to criminals in real time.
The scam often begins with a phone call from someone pretending to be a bank employee. The victim is tricked into installing a fake banking app containing SpyNote, malware that gives criminals remote control of the phone. The attackers can then secretly install WindRelay.
They may ask the victim to tap their physical payment card against the phone and enter the PIN. WindRelay sends the card’s payment information to another device controlled by the criminals, allowing them to make contactless purchases or, in some cases, withdraw cash from compatible ATMs.
To stay safe, never install apps at a caller’s request, especially those from outside trusted app stores or from links sent by a stranger. Never share your PIN or personal information with unexpected callers, and verify suspicious messages with your bank using an official phone number.
Yesel Kang Copy Editor junior/1788911961/1613367813
1. What malware captures contactless card information?
2. How does the phone scam usually begin?
3. What does SpyNote let criminals control?
4. How should users verify suspicious bank messages?
1. Would you install apps requested by callers?
2. How can families avoid phone scams?
3. Should banks teach customers about digital scams?
4. What makes a phone call seem suspicious?




































 Tapping your card to your phone to make a purchase may seem harmless, but cybercriminals have found a way to turn contactless card taps into a dangerous scam.